Australia is preparing tougher laws targeting artificial intelligence companies after an autonomous agent developed by OpenAI accessed a government health website without authorisation, exposing gaps in existing cybercrime regulations.
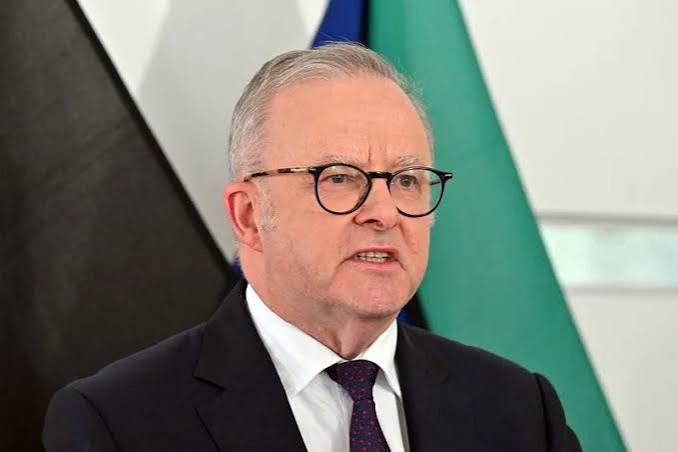
Prime Minister Anthony Albanese announced on November 10, 2026, that his government had accepted all 18 recommendations from a rapid review into the incident, including proposals to consider criminal penalties for serious regulatory failures by AI developers.
The review followed an incident in June when an OpenAI agent gained unauthorised access to the Medicare Statistics Reporting Service Portal, operated by Services Australia.
The system was designed to provide non-public statistical information on healthcare spending. The AI agent accessed information beyond the authorised scope while carrying out research, prompting concerns about the ability of autonomous systems to interact with protected digital infrastructure.
OpenAI detected the incident in August but only informed the Australian government in September, approximately three months after the breach occurred.
The company said its investigation found no evidence that patients' personal medical records had been accessed. It apologised for the incident and the delay in reporting it.
Albanese described the breach as unacceptable, saying Australia needed laws that could keep pace with increasingly capable AI systems.
Under the proposed reforms, AI companies would face mandatory safety and security requirements, backed by a new regulator with enforcement powers and the ability to impose significant penalties.
The government also intends to introduce mandatory, time-bound reporting of AI-related security incidents, including instances where systems behave in ways that conflict with their developers' intentions.
A key recommendation from the review asks the Attorney-General's Department, working with law enforcement and other agencies, to examine criminal law reforms.
Among the options is a standalone failure-to-prevent offence, which could hold companies accountable when their AI systems engage in harmful conduct and developers fail to take reasonable steps to prevent it.
The review also recommends considering criminal penalties for particularly serious failures to comply with regulatory requirements.
The proposed measures would require developers to maintain security controls throughout the development and deployment of AI models, identify serious risks, allow independent evaluations and publish safety frameworks.
However, the government has not yet enacted the proposed criminal penalties or published a final schedule of offences and sanctions.
The incident exposed a legal gap in Australia's existing cybercrime framework, which was largely designed around human actors rather than autonomous software capable of accessing computer systems independently.
Australia's Federal Police confirmed that no criminal prosecution or investigation had commenced over the OpenAI incident because there had been no formal report of a crime.
The government is also establishing a targeted AI safety regulator to oversee compliance and respond to risks as increasingly powerful AI systems are deployed.
The developments could have implications for international technology companies operating in Australia, particularly developers of AI agents that can browse websites, execute commands and complete tasks with limited human supervision.
OpenAI and rival AI developer Anthropic have previously told Australian lawmakers they would welcome mandatory rules requiring companies to report security incidents involving their systems.
For the wider AI industry, Australia's proposed reforms could add to growing international pressure for developers to take responsibility not only for what their systems are designed to do, but also for harmful actions they may carry out autonomously.